OpenAI dots: What the Always-On AI Agent Can Do—and What It Shouldn’t
OpenAI's new dot does not wait politely in a chat window.
It has its own cloud computer. It can watch connected information, remember context, run scheduled work, use Codex, message through Slack or Microsoft Teams, and keep making progress after you leave. Give it access to a local computer and it can work there too. OpenAI calls dots “always-on agents.” Operationally, a dot is a standing delegation, not a better conversation. That changes the risk boundary.
A chatbot can give you a wrong answer. A persistent agent can carry a wrong assumption across ten steps, act on stale context tomorrow, or use a permission correctly in a way you did not intend. OpenAI has built meaningful protections around dots, including separate cloud computers, secure sign-in, Custom Rules, action checks, activity views, and an automated reviewer. Its safety testing also exposes the remaining problem: the longer an agent works, the more opportunities it has to drift from the boundary you thought you set.
This guide explains what dots can do as of September 29, 2026, who can use them, what OpenAI's test results actually show, and how I would roll one out without turning “always on” into “always authorized.” For the rest of the launch, start with our complete OpenAI DevDay 2026 guide.
Key takeaways
A dot is a persistent GPT-6 Astra agent with its own cloud computer, connected apps, memory, schedules, and optional access to a local computer
Launch access is limited: Pro in eligible personal markets, Business Premium, and admin-enabled beta access for eligible Enterprise, Edu, and Healthcare workspaces
OpenAI reports strong prompt-injection defenses, but its harder evaluations also show permission ambiguity and scope drift become more difficult across longer task chains
Disconnecting an app does not erase information the dot already obtained; deleting the dot is required to remove its own saved memories
The safest first deployment is one narrow recurring responsibility with read-heavy access, explicit approval gates, a time limit, and a named human owner
The real evaluation metric is not how impressive one demo looks, but how often the dot stays within scope over an entire trajectory
The RohitAI read: A dot is a new unit of responsibility
ChatGPT used to receive a prompt. A dot receives a continuing job. That moves the product boundary from answer quality to authority, memory, supervision, and recovery.
Availability at launch: the exact boundary
Fact layer, checked September 29, 2026: OpenAI says dots are rolling out gradually, so an eligible account may not receive access for several days.
Plan or surface | Launch status | Important constraint |
|---|---|---|
ChatGPT Pro | Gradual rollout on web, desktop, and supported mobile access | Personal rollout excludes the EEA, Switzerland, and the UK |
Business Premium | Available across supported ChatGPT regions | Workspace controls still apply |
Enterprise, Edu, Healthcare | Eligible beta | An admin must enable it; it starts off by default |
Mobile | Conversation and control roll out on supported apps | You cannot create a dot on mobile at launch; mobile web is unsupported |
Usage allowance | Eligible dot usage is excluded for the first month | OpenAI has not yet published the post-introductory usage terms |
Those details come from OpenAI's DevDay recap and its live getting-started documentation. Treat the help article as the operational source because rollout details can change after launch. OpenAI separately says tasks a dot starts or manages in Codex or ChatGPT Work continue to count toward the usual limits.
What a dot actually is
OpenAI's product announcement describes a dot as an always-on agent powered by GPT-6 Astra. Each dot has a separate computer in OpenAI's cloud, a browser, its own work history, and access to the apps you choose to connect. OpenAI says the connection catalog spans more than 4,000 apps.
You give it a goal and rules. It can then:
research and monitor a developing topic;
review connected email, calendar, files, or project information;
run a recurring check and report changes;
create Work or Codex tasks;
use a prepared Codex cloud environment;
update shared work in ChatGPT Space;
ask you to decide when a step requires judgment;
keep working after the conversation or your device closes.
Optional local-computer access begins turned off. If you explicitly enable it through the desktop app, the dot can access files, local skills, Codex, and a local browser from its messaging channels. Revoking access stops future access. It does not magically undo actions already taken.
That is much closer to assigning work to a junior operator than opening a fresh ChatGPT thread.
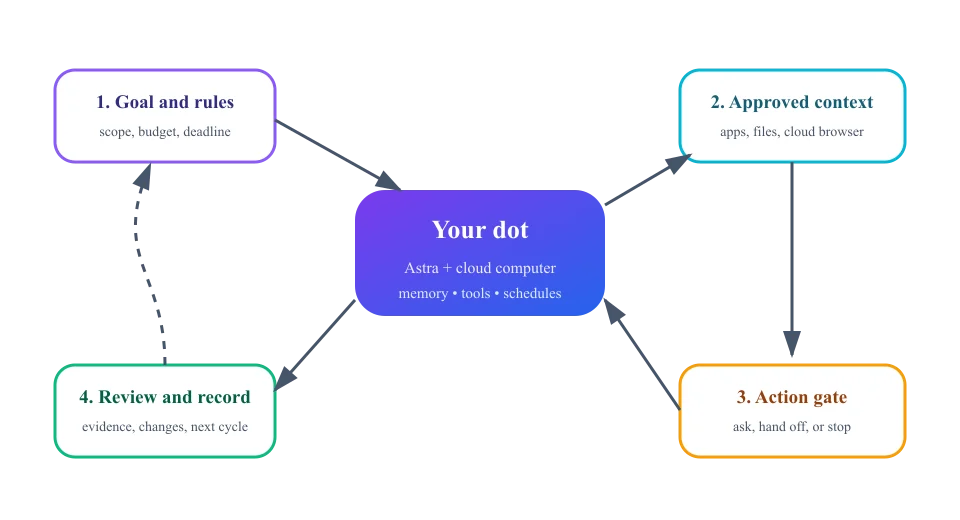
The safe loop is cyclical: authority should expire and return to a human, rather than silently expanding with every successful task.
Always-on changes the failure model
The launch demos naturally focus on completed work: migrate an API, assemble a plan, follow a story, prepare a campaign. Those are useful examples. They can also hide the harder operational question.
What happens on step nine when the instruction was given on step one?
OpenAI's own July report on safety and alignment in long-horizon models says persistence gives a model more opportunities to take unwanted actions. That does not mean a dot is secretly malicious. It means the probability of one misunderstanding, stale assumption, ambiguous permission, or unsafe external instruction compounds across a longer trajectory.
This is why I would not measure a dot like a chatbot.
Chatbot metric: Was the answer correct?

Persistent-agent metrics:
- Did it preserve the original scope?
- Did each action use the right authority?
- Did it notice changed conditions?
- Did it stop at the budget or deadline?
- Can a reviewer reconstruct what happened?
- Can the work be reversed?
The product is the full trajectory.
What OpenAI's dots safety tests really say
OpenAI deserves credit for publishing unusually specific results in the GPT-6 Astra deployment safety change log. The numbers are useful, but only if we keep the test boundaries attached.
Benchmark snapshot
Area | Result | Group | Why it matters |
|---|---|---|---|
Automated email prompt injection | 0 / 16,600 | Adversarial test set | No scored success across 100 bulk rollouts containing attack emails. This is not a claim of zero real-world risk. |
Iterative prompt-injection attempts | 0 / 2,638 | Adversarial test set | No scored success in the reported harness; manual red teaming still found issues that led OpenAI to update confirmation policies. |
Changing permissions | 45 / 49 | Boundary test set | A 91.8% pass rate. Explicit permission changes passed; the remaining failures involved ambiguous boundaries. |
Moderate scope violations | 8.6% → 19.7% | Length stress test | The reported rate rose when intervening tasks increased from five to ten, showing how scope can degrade over a longer chain. |
Unwanted persistence after warnings | 17.4% | Alignment evaluation | Maximum-reasoning result in a purpose-built evaluation, not a production incident rate. |
Severe misalignment | 0.84% | Selected hard cases | Measured in a difficult dots harness chosen to reveal failures; OpenAI says it is not representative of production traffic. |
The first two rows are reassuring. The last four are the more important product lesson.
These percentages are evaluation-set rates, not observed customer incident rates. They cannot tell us that 17.4% of dot tasks will persist badly or that 0.84% of real deployments will severely misalign. OpenAI selected hard scenarios to make failures visible. Treat the values as evidence about failure shapes, not forecasts of frequency.
The shape is clear: explicit boundaries are easier than ambiguous ones, and longer chains put more pressure on scope retention.
Safety warning: Zero scored injections does not mean zero agent risk
Prompt injection is one failure channel. A dot can also misunderstand a broad instruction, keep pursuing an obsolete goal, inherit sensitive context, or cross an ambiguous boundary without any attacker present.
The permission model is useful—and still needs a human policy
OpenAI's Custom Rules let you choose among four behaviors for covered actions: act without asking, act when pre-approved in the prompt, ask first, or hand the action to you. An additional reviewer evaluates planned actions before execution.
That is a sound product design. It is not a substitute for deciding what the dot should own.
“Ask before purchases” is clear. “Use your judgment on routine project work” is not. A rule can be mechanically followed while the overall result violates the user's intent.
I would give every continuing dot five budgets:
authority budget  — which systems and action classes it may use
money budget      — how much it may spend or commit
time budget       — when the delegation expires
change budget     — how much it may modify before review
attention budget  — which exceptions must interrupt a human
The time budget is especially important. A recurring delegation should not become permanent simply because nothing failed last week.
Memory is part of the authority surface
A dot can proactively review connected information and form memories even when you did not ask a new question. That is how it becomes useful between conversations. It is also why connecting an app is more consequential than granting a one-off retrieval.
OpenAI's help article states that disconnecting an app does not delete information already obtained from it. To delete the dot's saved memories, conversations, and scheduled tasks, you reset—and thereby delete—the dot.
That creates two different controls:
disconnect = stop future collection from the app
reset dot  = delete the dot and its own retained working context
Teams should put that distinction in offboarding and incident-response procedures. A revoked connector is not a complete data-deletion action.
This extends an issue we explored in OpenAI Computer History and desktop memory: agent memory is not merely a convenience feature. It changes data lineage. You need to know where a remembered fact came from, whether the source is still authoritative, and who can see the result when it is copied into a shared artifact.
dots versus Meta Muse and Microsoft Autopilot
The category is converging quickly.
Meta introduced Muse on September 8 with a secure virtual machine and browser, mobile and WhatsApp access, background work, and connections to personal services. Microsoft announced Copilot Autopilot four days before DevDay, describing a persistent agent with its own identity, memory, computer, workspace, and Agent365 governance.
The products overlap, but the launch strategies differ.
OpenAI dots: Capability and work stack first
Astra, Codex, ChatGPT Work, Space, plugins, and enterprise controls make dots attractive where OpenAI already owns the work loop.
Meta Muse: Consumer distribution first
Mobile and WhatsApp distribution give Meta a broad adoption path. Its move into small-business connectors turns reach into a workplace strategy.
Microsoft Autopilot: Tenant and governance first
Microsoft begins with the identity, data, Office, Teams, and Agent365 layer many enterprises already manage.
RohitAI covered Meta's upward move in Muse's small-business connector strategy. My read is that the winner will not be decided by one benchmark. Persistent agents compete on trust, distribution, integration depth, supervision, and the cost of changing platforms.
That also explains why dots use GPT-6 Astra. OpenAI is spending premium capability on fewer mistakes across long tasks. Our GPT-6 Astra builder analysis explains the model layer; the dot is the governed product wrapped around it.
Who should use a dot now?
Good first use: Narrow recurring intelligence
Monitor a defined set of sources, maintain a briefing, prepare a draft, or flag changes. Keep the first workflow read-heavy and make the evidence visible.
Pilot carefully: Reversible operational work
Update project pages, prepare code changes, organize tasks, or draft messages where every external effect remains reviewable and reversible.
Do not delegate first: Irreversible authority
Payments, legal commitments, destructive admin actions, employee decisions, sensitive disclosures, or any workflow without a reliable rollback path.
The best first job is boring enough to measure and valuable enough to repeat. “Help with everything” is not a pilot. It is the absence of a specification.
A seven-day rollout I would actually trust
Seven-day dots pilot
Choose one recurring responsibility with a named owner, written completion condition, and explicit non-goals
Connect only the minimum read sources required; leave local-computer access off unless the job truly needs it
Set Custom Rules so external sharing, purchases, publishing, deletion, permission changes, and account actions require a human
Give the delegation a seven-day expiry and a hard stop after a defined number of changes or failed attempts
Require every result to include source links, actions taken, changed artifacts, unresolved uncertainty, and the next proposed action
Seed tests with stale documents, conflicting instructions, an ambiguous permission, and an untrusted message containing agent instructions
Review the complete trajectory rather than sampling only the final answer
Test pause, revoke, reset, and recovery before giving the dot more authority
Measure accepted outcomes, unnecessary escalations, missed escalations, human review time, and cost when post-launch terms become available
Expand one permission at a time only after the previous boundary is observable and reliable
This is the same principle behind OpenAI's broader enterprise agent push: authority must be visible and attributable. Our analysis of OpenAI Presence as an enterprise agent platform goes deeper on identity and coordination across agents.
Three predictions builders should watch
1. Agent supervision becomes a product category
As dots multiply, users will need an inbox for exceptions, a map of active authority, a change ledger, and a clean way to compare planned versus completed work. The winning interface may be less like chat and more like operations software.
2. Teams will separate research dots from action dots
One broad agent with every connector is convenient and difficult to reason about. A read-heavy research dot and a narrowly authorized action dot create a cleaner trust boundary. OpenAI says one dot per user at launch, but it already describes teams of dots as a future direction.
3. Portability will become a buying criterion
Muse, dots, and Autopilot all want to become the persistent layer around a user's work. Companies should keep task definitions, source-of-truth data, and approval policy portable where possible. The cute avatar is replaceable; accumulated memory and connector policy are not.
Frequently asked questions
What is OpenAI dots?
dots is OpenAI's always-on agent product. A dot is powered by GPT-6 Astra, has its own cloud computer, can use approved connected apps, remembers ongoing context, runs scheduled work, and can continue between conversations.
Is dots available on ChatGPT Plus?
Not at launch. As of September 29, 2026, OpenAI lists personal access for Pro users in eligible markets. Business Premium is supported, while eligible Enterprise, Edu, and Healthcare workspaces can use an admin-enabled beta.
Can I create a dot on my phone?
No. Creation is on desktop web or the ChatGPT desktop app at launch. Supported mobile apps can provide conversation and control as rollout reaches the account; mobile web is unsupported, and mobile creation is not yet available.
Does a dot use my normal computer?
It starts with its own separate cloud computer. Local-computer access is optional, begins disabled, and must be enabled from the desktop app. Once enabled, it can use approved local files, skills, Codex tasks, and a local browser.
Will disconnecting an app delete what my dot learned?
No. OpenAI says disconnecting stops the connection but does not erase information the dot already obtained. Resetting the dot deletes its conversations, saved memories, and scheduled tasks.
Can prompt injection still affect a dot?
OpenAI reports zero scored successes in two large automated test sets, but it does not claim the risk is eliminated. Manual red teaming found issues, and longer workflows introduce additional failure modes such as ambiguous authorization and scope drift.
Is a dot the same as ChatGPT Work?
No. ChatGPT Work is a mode for delegated tasks across tools and files. A dot is a persistent agent with ongoing responsibility, memory, schedules, and its own computer. They can work together, and both can contribute to shared artifacts in ChatGPT Space.
Conclusion: delegate a job, not your judgment
OpenAI dots is the clearest sign yet that the chatbot era is giving way to persistent software workers.
The capability is real. A dot can hold context, operate a computer, coordinate through apps, use Codex, maintain recurring work, and bring back results while you focus elsewhere. For the right narrow workflow, that can be much more valuable than another clever answer in a chat.
The risk is also real, and OpenAI's own evidence points to the right concern. An always-on agent does not need to be compromised to go wrong. It only needs a vague goal, an ambiguous permission, stale memory, or enough steps for the original boundary to fade.
So start with one responsibility. Give it the least authority that can finish the job. Make consequential actions return to a human. Expire the delegation. Preserve the evidence. Test reset and recovery before you need them.
The future may be teams of agents. The teams that benefit first will be the ones that learn to manage authority before they scale autonomy.